

Tencent's CubeSandbox Boots Isolated AI Agent VMs in Under 60ms
Tencent open-sources CubeSandbox, a Rust-built microVM sandbox for AI agents that cold-starts in under 60ms with hardware-level isolation and drop-in E2B compatibility
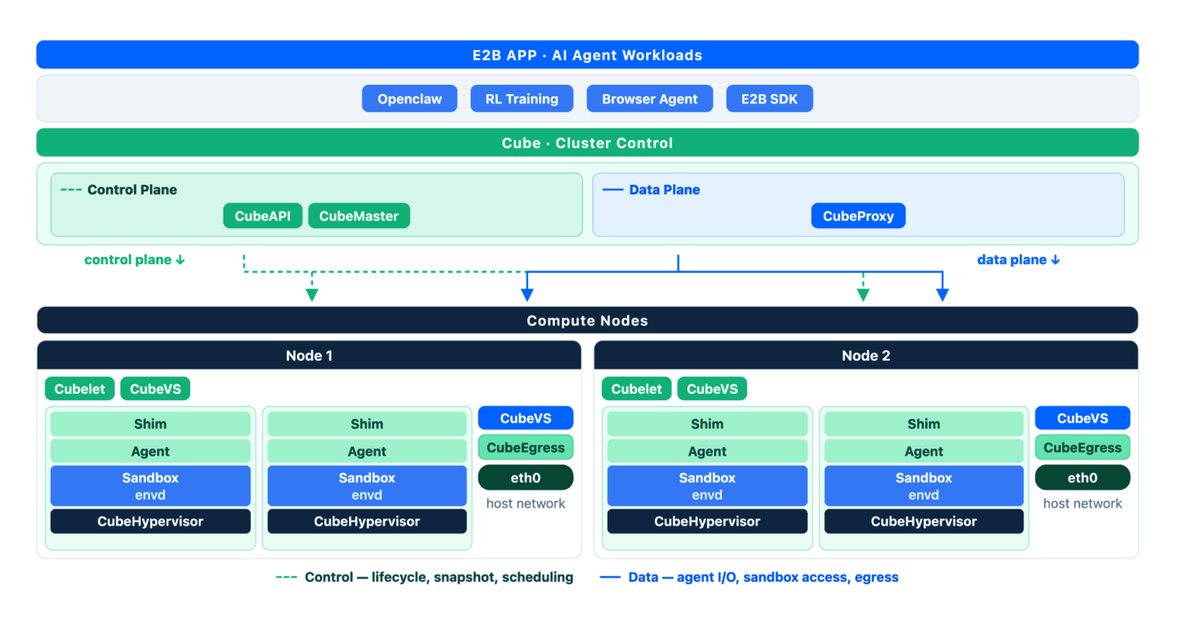 PRO
- Tencent Cloud open-sourced CubeSandbox, a Rust-built microVM sandbox for AI agents under Apache 2.0.
- Each sandbox boots a dedicated OS kernel via KVM in under 60ms cold start, with under 5MB memory overhead per instance.
- Drop-in replacement for E2B: swap one environment variable, zero code changes required to migrate.
- Built on a custom VMM (not Firecracker) with resource pool pre-provisioning, snapshot cloning, and EPT Lazy Load for speed.
- CubeVS provides eBPF-based kernel-level network isolation with L7 egress filtering and credential injection per sandbox.
- Validated at Tencent Cloud production scale; supports 2,000+ sandboxes on a single 96-vCPU host with 90%+ storage savings.
Running AI agent code safely is one of the hardest unsolved problems in production agent infrastructure. Agents write code that can't be reviewed before it runs, call tools with wrong arguments, and sometimes try to delete your filesystem. The standard answer has been Docker containers, but containers share the host kernel, and a kernel-level exploit can escape the container entirely. CubeSandbox is Tencent Cloud's answer: a fully open-source, hardware-isolated sandbox service that boots a dedicated microVM per agent in under 60ms, uses less than 5MB of memory overhead per instance, and is a drop-in replacement for E2B.
The problem with the status quo
The agent sandbox market has been growing at a staggering pace. E2B alone went from 40,000 sandbox sessions per month in March 2024 to roughly 15 million per month by March 2025. But the dominant approaches all make uncomfortable tradeoffs:
- Docker containers are fast but share the host kernel. Docker containers possess a risk of providing incomplete isolation, either independently, or when used in combination with kernel vulnerabilities.
- Traditional VMs give you a dedicated kernel but take seconds to boot, making them unusable for tight agent loops.
- Hosted services like E2B abstract the infrastructure but lock you into their cloud, their pricing, and their data residency rules.
Agents work in tight loops , generate, execute, evaluate, iterate. If sandbox creation takes 10+ seconds, the agent stalls. The ideal sandbox needs VM-level isolation at container-level speed, and it needs to be cheap enough to run thousands of instances concurrently.
What CubeSandbox actually is
Cube Sandbox is a high-performance, out-of-the-box secure sandbox service built on RustVMM and KVM. It is the industry's first open-source sandbox service that combines hardware-level isolation with sub-100ms startup. Instead of wrapping Docker, the team implemented a VMM from scratch in Rust, optimized specifically for AI agent scenarios.
The key insight is that Firecracker, the microVM powering E2B, is a general-purpose VMM. Firecracker is a general-purpose MicroVM, and its startup process includes many steps unnecessary for agent sandbox scenarios. The CubeSandbox team performed full-link tailoring: they minimized the device model to only retain virtual devices essential for sandbox scenarios (virtio-net, virtio-blk, serial), and built a customized guest kernel that retains only the minimal feature set required for agent execution, drastically shortening the kernel boot path.
This story is for Pro members
You've reached the end of the free preview. Upgrade to AlphaSignal Pro to read the full article - and everything else behind the paywall.
Comments
