

Zed v1.14 Locks Down AI Agents With OS-Enforced Sandboxing by Default
Zed v1.14 ships OS-enforced sandboxing for its AI agent's terminal and fetch tools, blocking rogue writes and network calls by default
- Zed v1.14 ships OS-enforced sandboxing for the AI agent's
terminalandfetchtools, enabled by default for all users. - Default sandbox blocks writes outside project directories, writes to
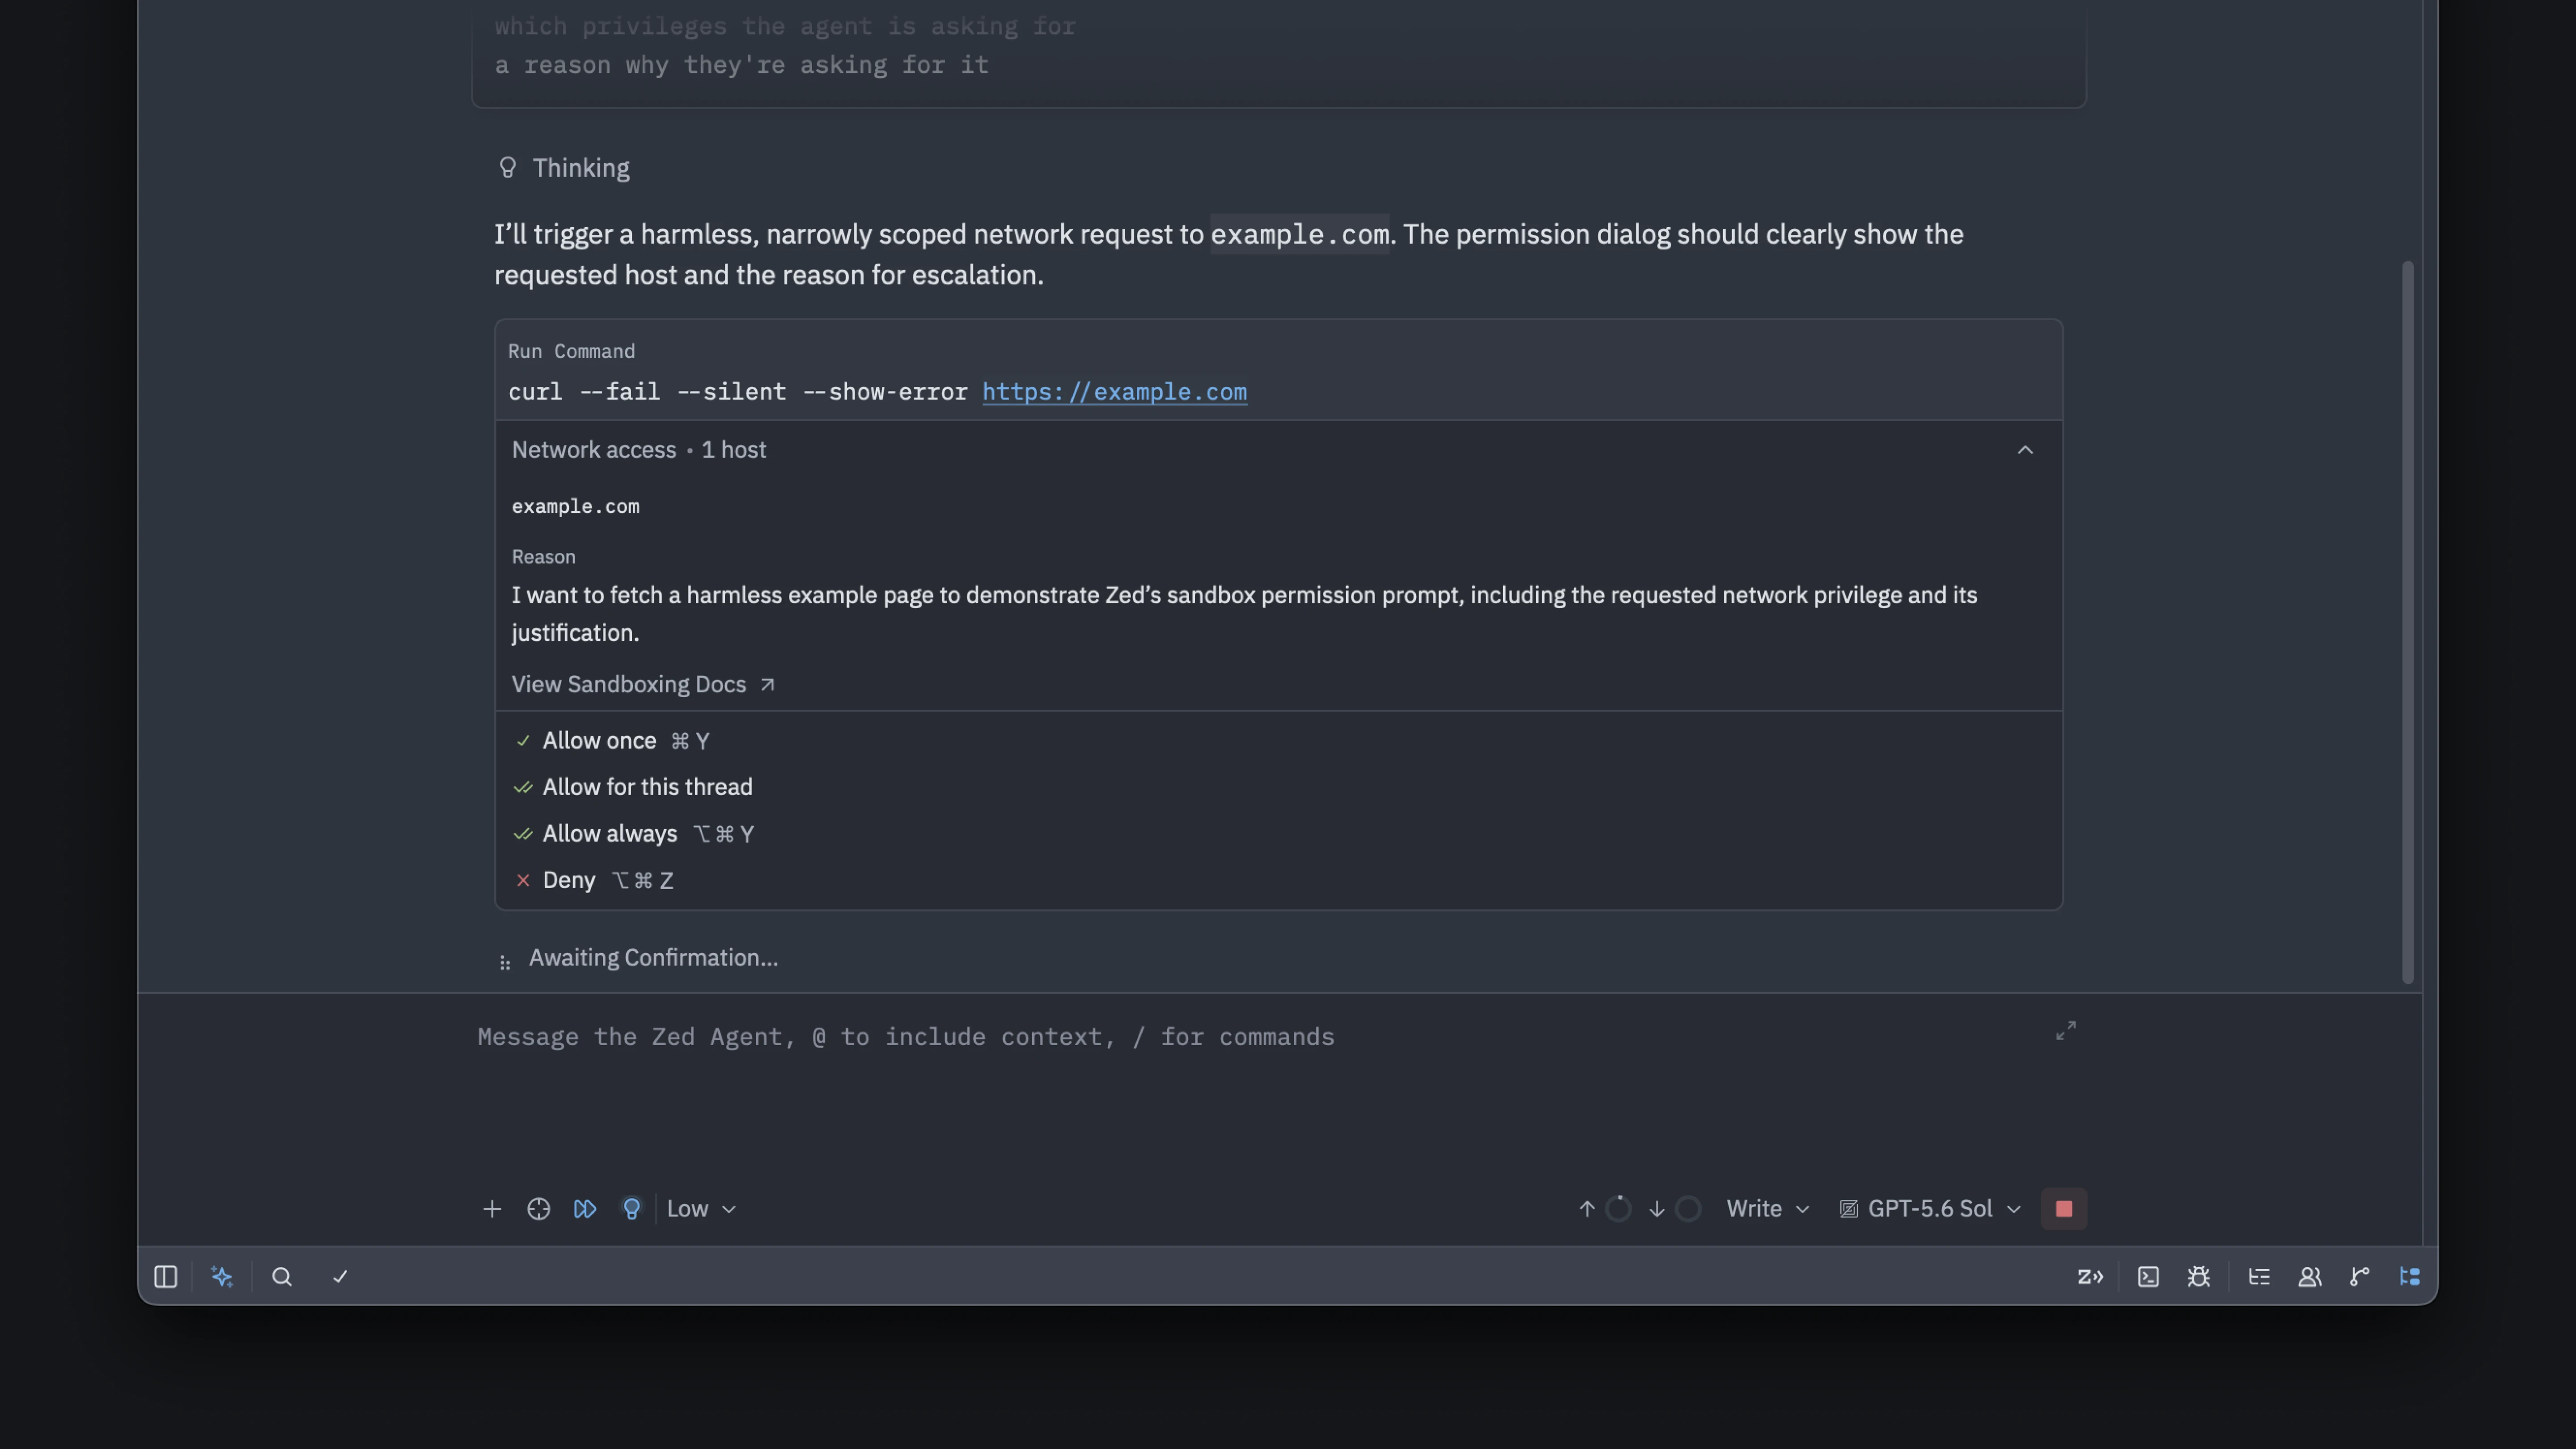
.git, and all outbound network requests. - Agents can request elevated permissions with a reason; users choose to allow once, for the thread, always, or deny.
- Platform implementations: macOS uses Seatbelt, Linux uses Bubblewrap (
bwrap), Windows requires WSL. - Sandbox does not cover normal terminal tabs, language servers, extensions, or external agents — only the Zed Agent's built-in tools.
- Also in v1.14: Project Panel undo/redo for file operations, Skip Hooks toggle in Git Panel, configurable Agent Panel fonts. Full changelog
Zed v1.14 ships with OS-enforced sandboxing for the AI agent's terminal and fetch tools. The operating system physically blocks access to resources the agent was never supposed to touch, with no reliance on the model following instructions.
Why trusting your agent isn't enough
Agentic coding tools carry a structural tension: give the agent too little freedom and you spend your time approving every command; give it full access and a single rogue prompt injection can cause real damage. Instruction-following helps, but it offers no protection against prompt injection attacks, where malicious content in the environment hijacks what the agent does next.
The threat is already documented. Imagine reviewing a contributor's PR on an open source project. You open an agent and ask it to review the diff. The PR contains a modified AGENTS.md that instructs your agent to upload $MY_SECRET_API_KEY to an attacker-controlled server. This class of attack has been observed in the wild.
What the sandbox actually does
The sandbox restricts what the agent can do when using the terminal and fetch tools. Enforcement happens at the OS level. The default rules are tight:
- No writes outside project directories
- No writes to
.git - No outbound network requests
Sandboxing is on by default in v1.14. No configuration required.
When the agent needs more access, it requests it explicitly. A permission prompt shows which privilege is being requested and why, with four options: allow once, allow for this thread, allow always, or deny.
OS primitives, not rule lists
Earlier versions of Zed used fine-grained rules, such as blocking commands matching git .*. Rules are trivially bypassed. An agent that wants to touch your .git folder can call bash -c 'git ...', write a small Python script, or use any number of shell tricks. The new sandbox uses OS-level features to restrict which resources a tool call can reach at all. If the agent attempts to access a restricted resource, the OS blocks it.
The implementation varies by platform:
- macOS: Uses Seatbelt, Apple's built-in sandbox framework
- Linux: Uses Bubblewrap (
bwrap), which creates isolated namespaces via the Linux kernel - Windows: Uses WSL; non-WSL shells on Windows do not support sandboxing
Linux users need a working bwrap binary without the setuid bit set in their $PATH. macOS and the fetch tool on all platforms have no extra requirements.
The symlink swap attack
The sandboxing blog post covers one particularly tricky implementation problem: the symlink swap attack, a classic TOCTOU (time-of-check-time-of-use) vulnerability. TOCTOU bugs arise when there is a gap between when a system checks a permission and when it actually uses the resource, and an attacker exploits that window to swap what the path points to.
A malicious agent could request write access to /foo/bar, get the user to approve it, then race to replace /foo/bar with a symlink to /home/alice in the window between approval and sandbox configuration. The sandbox would then mount the real home directory with write access. The timing window is tiny, typically a few hundred microseconds to spawn a subprocess, but an attacker can try repeatedly and only needs to win once. Zed's sandbox detects this attack and fails closed: the untrusted command simply does not run.
What the sandbox does not cover
The Zed team is upfront about the limits. Sandboxing applies only to Zed Agent's terminal and fetch tools. It does not cover Zed itself, language servers, extensions, tasks, normal terminal tabs, External Agents, or Terminal Threads.
A sandboxed agent can still cause harm through indirect paths:
- Adding a
build.rsthat runs malicious code when you runcargo runoutside the sandbox - Editing your
.bashrcif it has write access to your home directory - Installing a Git hook that fires when you commit from a regular terminal
- Embedding a malicious Rust procedural macro that executes during
rust-analyzerbuilds
The Zed team frames sandboxing explicitly as one layer in a defense in depth strategy: multiple overlapping controls rather than a single complete barrier.
Everything else in v1.14
The release also adds undo/redo for file operations in the Project Panel, a Skip Hooks toggle for commits, and configurable Agent Panel fonts:
- Project Panel undo/redo: Moves, renames, and deletes can now be undone and redone in both local and remote projects.
- Skip Hooks toggle: A new toggle in the Git Panel lets you bypass
pre-commitandcommit-msghooks without touching your git config. - Configurable Agent Panel fonts: The agent panel now accepts a custom font independent of your editor font.
Zed v1.14 is available now as a free download on macOS, Linux, and Windows.
Comments
