

Factory's Droid Now Catches Real Security Bugs Before They Ship
Factory's Droid now runs a STRIDE-based security scan on every PR automatically, and has already surfaced a real CVE in a popular Kubernetes operator.
- Factory's Droid now runs a STRIDE-based security review on every non-draft PR automatically, alongside standard code review.
- Findings include severity rating, CWE reference, plain-language explanation, and an inline suggested fix posted directly on the diff.
- Coverage spans OWASP Top 10, OWASP LLM Top 10 (including AI-specific vulnerabilities), and supply-chain analysis.
- Droid responsibly disclosed CVE-2026-42876 in the External Secrets Kubernetes operator, a privilege escalation flaw fixed in v2.4.1.
- Available on all plans starting at $20/month; activate with
automatic_security_review: trueor run/security-reviewon demand. - A deep audit mode uses orchestrated multi-agent missions to scan every source file and validate exploitability before reporting.
Security bugs are sneaky. They rarely announce themselves as architectural disasters -- they hide in a missing auth check, a user-controlled string that crosses a trust boundary, or a token that quietly ends up in a log file. The most dangerous security bugs often look like ordinary code review details: a missing authorization check, a user-controlled string crossing a trust boundary, or a token logged where it should never appear. Factory's AI coding agent, Droid, just got a dedicated layer to catch exactly these issues before they ship.
Security baked into every PR, automatically
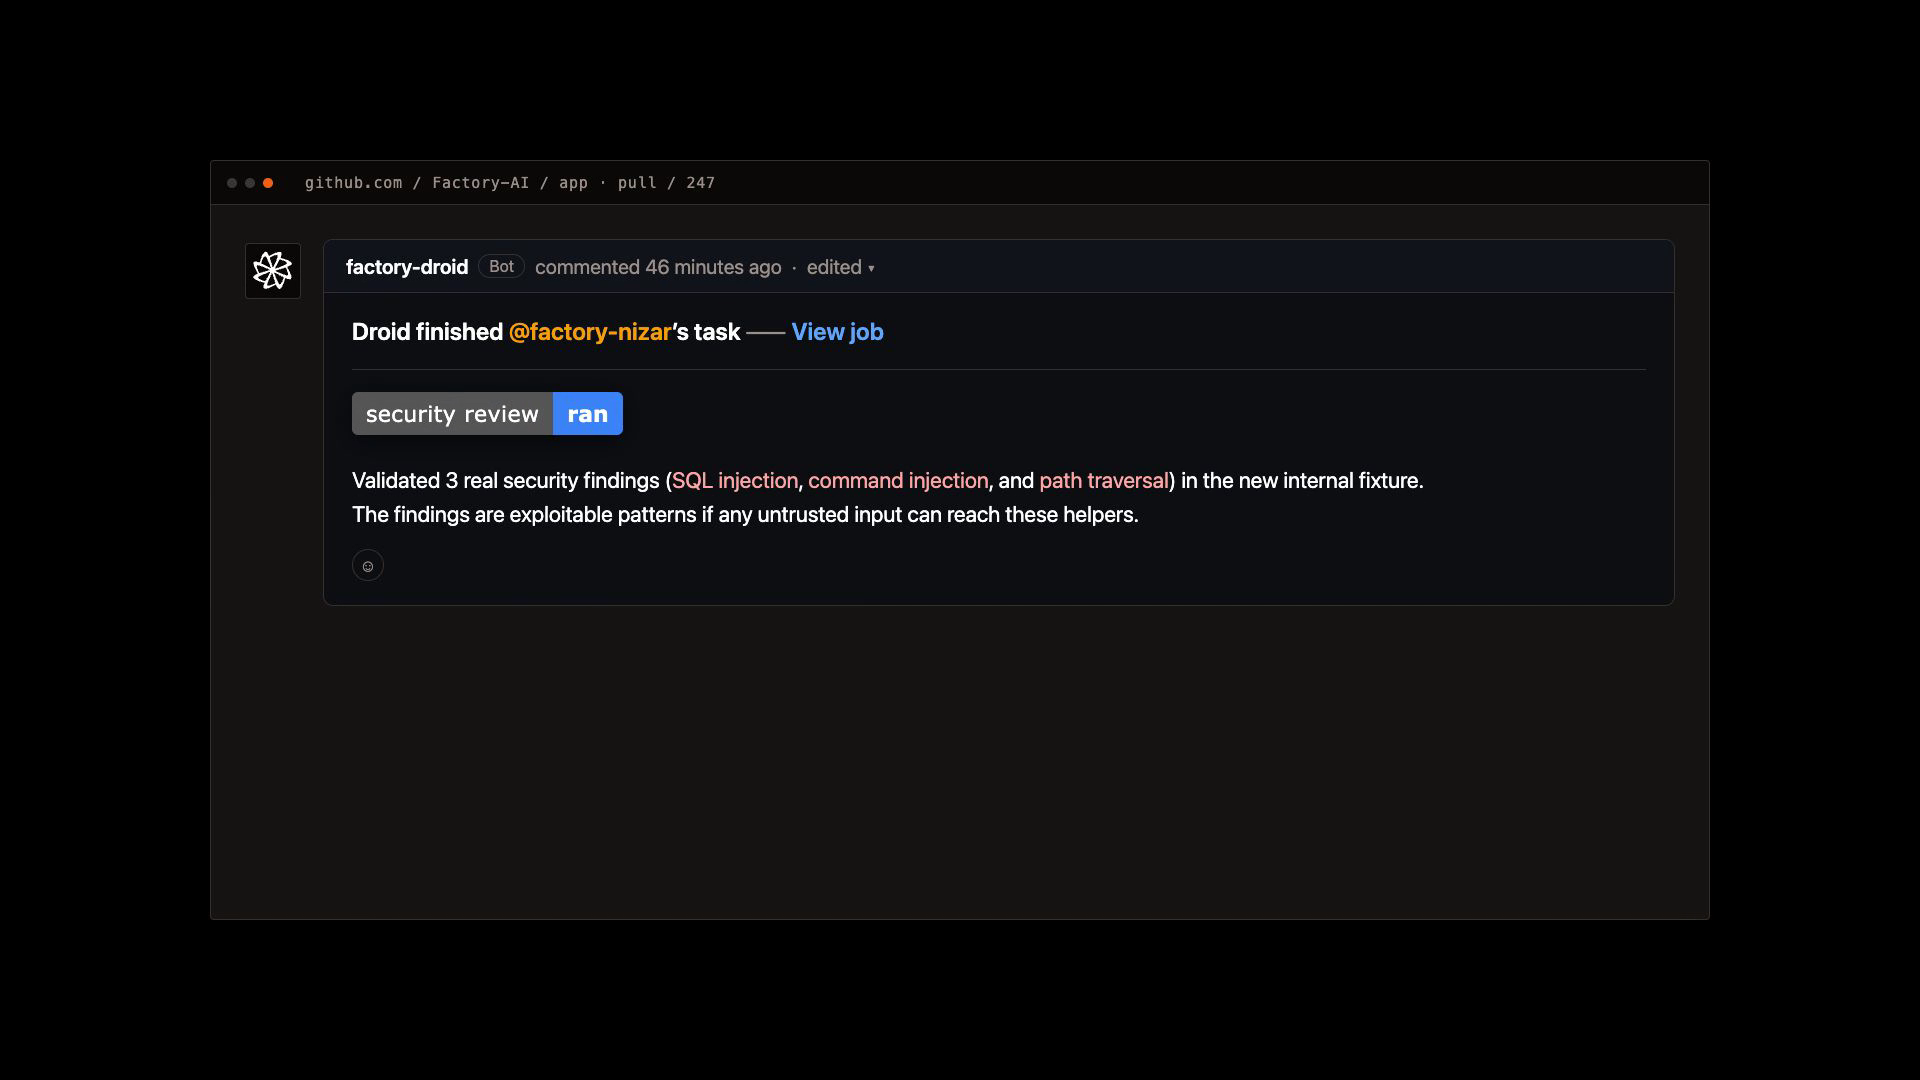
On every non-draft PR, Droid now runs a STRIDE-based security review alongside the standard code review. Findings come back with severity, a CWE reference (a standardized identifier for vulnerability classes), an explanation, and a suggested fix, posted as inline comments directly on the diff.
STRIDE is a threat modeling framework developed at Microsoft that categorizes threats into six buckets: Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. It gives the scanner a structured lens for thinking about what an attacker could actually do with a piece of code, rather than just pattern-matching on known bad patterns.
Droid runs a security-focused review using STRIDE methodology along with OWASP Top 10 and OWASP LLM Top 10 checks. The OWASP LLM Top 10 coverage is particularly notable -- it means the scanner is aware of AI-specific attack surfaces like prompt injection and insecure output handling, which most traditional static analysis tools completely miss.
How it actually works under the hood
The security review uses specialized Factory skills installed from the public Factory-AI/skills repository: threat-model-generation, which generates STRIDE-based threat models for repositories, and commit-security-scan, which scans code changes. These are modular, composable skill definitions that Droid loads and executes as part of its review pipeline.
The process isn't just a single-pass scan. For the best coverage, Droid runs a deep security audit across an entire repository. This uses orchestrated multi-agent missions that scan every source file, cross-reference findings, and validate exploitability before reporting. That validation step is key -- it's what separates this from a noisy static analyzer that drowns you in false positives.
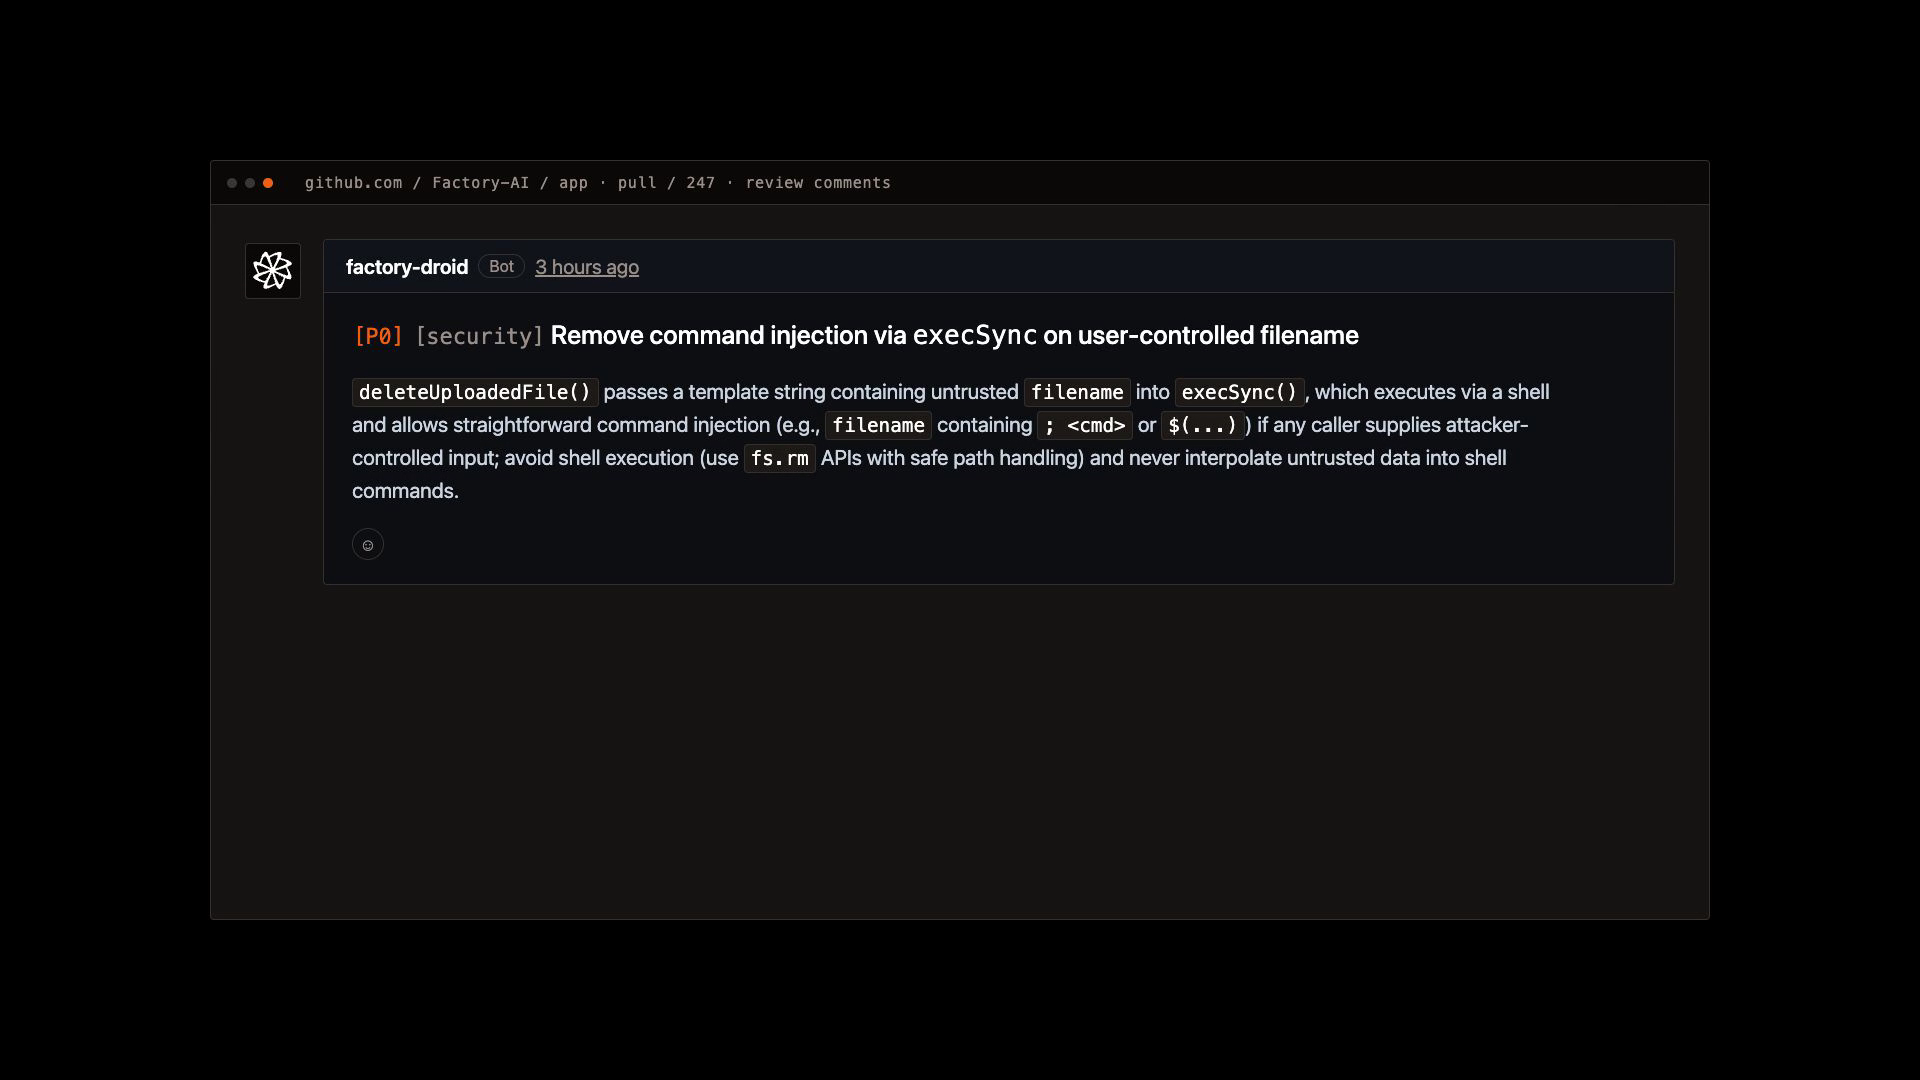
The findings are structured and actionable:
- A priority tag (P0 through P3)
- The affected area and symbols
- A plain-language explanation of the vulnerability
- A CWE reference for cross-referencing with vulnerability databases
- An inline suggested fix posted directly on the diff
Real CVEs, not toy examples
The most compelling part of this launch isn't the feature itself -- it's the receipts. Droid security review has been run across production codebases, surfacing findings that went through responsible disclosure. Two of those findings are now public.
The more serious of the two is CVE-2026-42876 in the External Secrets Operator, a widely-used Kubernetes project. A user with only the permission to create ExternalSecret resources can force the External Secrets Operator to generate a standard Kubernetes Secret resource. This newly created Secret is then automatically populated by the Kubernetes API with a long-lived authentication token for a specified Service Account. Crucially, the attacker does not require direct create permissions on TokenRequest or Secret resources to trigger this behavior. In other words: a low-privilege user could quietly mint tokens that let them impersonate any service account in the namespace. The fix requires upgrading to version 2.4.1 or above.
The second finding hit the WorkOS Node SDK. Droid discovered that the SDK was re-serializing request bodies before running HMAC signature verification -- meaning it was modifying the data it was supposed to be verifying. The result: some valid webhook events were being rejected, and the signature check was silently broken.
Getting started
There are three ways to use Automated Security Review:
- Automatic on every PR: Set
automatic_security_review: truein your auto-review workflow to run the security pass on every non-draft PR alongside the standard code review (the two run concurrently). - On-demand via CLI: Run
/security-reviewin any Droid session to audit the full repo or just the current diff. - Full deep audit: Run
/security-review deep auditinside a Mission for an orchestrated multi-agent scan of the entire codebase.
Setup is a one-time operation. Run /install-code-review in the Droid CLI or Desktop App -- for GitHub repositories, the setup flow checks the Factory Droid GitHub App installation as part of configuring review automation. GitLab is also supported. Everything runs inside GitHub Actions using your Factory API key, so the bot never leaves your repository and operates with the permissions you grant.
You can also tune the depth of each review. The deep preset offers thorough analysis with higher reasoning effort, catches more subtle bugs but costs more per review, and is best for production code and security-sensitive repos. The shallow preset is faster and more cost-effective, covering surface-level issues -- good for high-volume repos, draft PRs, or teams watching spend.
Pricing and availability
Automated security review is available today on all plans. Factory's plans run Pro at $20, Plus at $100, and Max at $200 per month. No free Factory tier currently exists, requiring Pro at $20/month as the minimum entry point. Enterprise plans with custom seats, dedicated compute, and on-premise deployment are available through sales.
The bigger picture here is Factory's stated ambition: security review is the first line of defense, but building software autonomously means applying the same rigor at every step -- a complete development system where every stage is automated, verified, and continuously improving. Automated security review is one piece of that vision, but it's the piece that's hardest to argue against. If an AI agent is going to write and merge code autonomously, having it also audit that code for exploitable vulnerabilities before it ships is table stakes.
Comments
